Waslوصل
Every delivery.
A verifiable trace.Signed webhooks sent to a controlled HTTP receiver, with persistent attempts, receipt deduplication and bounded retry recovery.
The brief
An event can arrive twice, fail signature checks or meet a temporarily unavailable destination. Each outcome needs a clear, testable response.
The approach
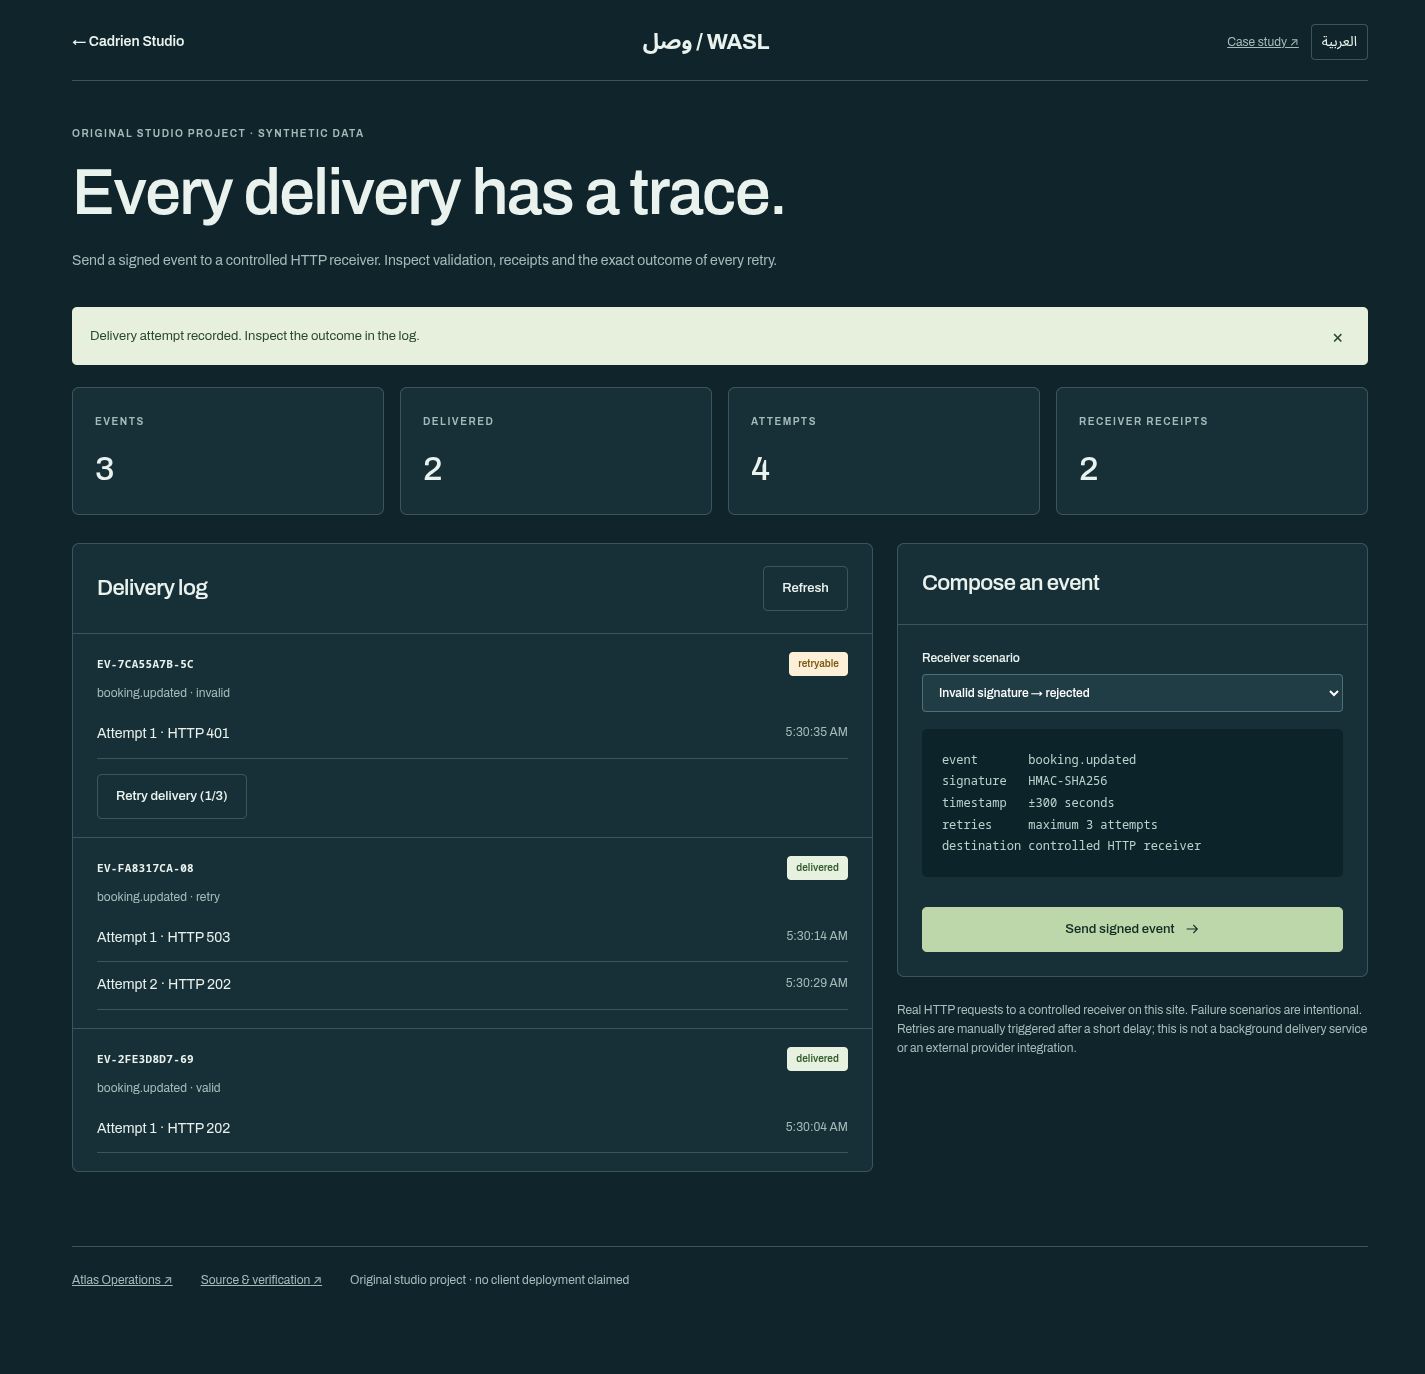
Wasl signs each delivery attempt, validates the body and timestamp at the receiver, persists receipts and records response codes. Deliberate receiver failures expose retry behavior.
What you can verify
- Send a valid event and inspect its HTTP receipt.
- Reject an invalid signature or expired timestamp.
- Trigger a temporary failure, retry and see the successful receipt.
- Follow permanent failure to its three-attempt limit.
- Inspect persisted attempts, idempotency and interrupted-delivery recovery.
Implementation & handoff
A live sender and receiver with durable event state, three-attempt limit, expiring delivery leases and recovery for interrupted attempts. Tests include invalid signatures, delayed retries and receipt integrity.
Honest context
A controlled integration lab on this site. Failure scenarios are intentional and retries are manually triggered. No external provider account, background scheduler, email delivery or security certification is claimed.